Retail and Accounting Made the Top 5 for Data Breaches
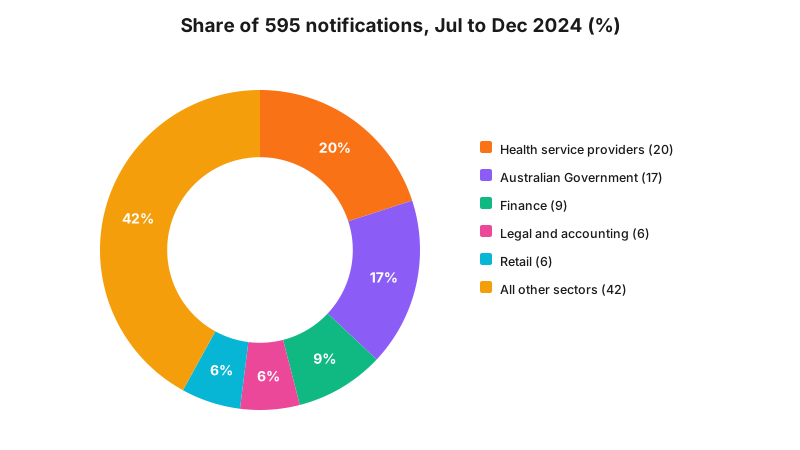
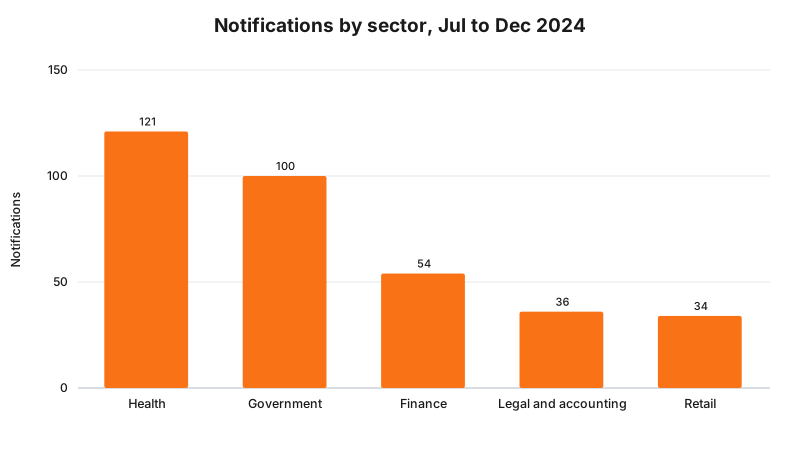
The OAIC's July to December 2024 report put health on 121 notifications, then government on 100, finance on 54, legal, accounting and management services on 36, and retail on 34. Here is what the list says about local businesses.
 Vikas Thakur Founder, RockingWeb 4 min read
Key takeaways
- The top 5 sectors made 345 of 595 notifications from July to December 2024, or 58%
- Health service providers led with 121 notifications (20%)
- Legal, accounting and management services reported 36 (6%), and retail reported 34 (6%)
- The OAIC counts notifications from covered entities, so a sector’s rank is not a security score
- Most small businesses with turnover of $3 million or less are outside the scheme unless an exception applies
The OAIC’s July to December 2024 report shows 345 of 595 breach notifications, or 58%, came from five sectors, and two of them are everyday local trades: retail, and legal, accounting and management services.
If you run a shop in Baldivis or an accounting practice in Cockburn, that list will look familiar. This post reads the table plainly, says what it can and cannot tell you, and links to the checks that matter for your own site.
The top 5, in numbers
| Sector | Notifications | Share of all notifications |
|---|---|---|
| Health service providers | 121 | 20% |
| Australian Government | 100 | 17% |
| Finance (including superannuation) | 54 | 9% |
| Legal, accounting and management services | 36 | 6% |
| Retail | 34 | 6% |
| Top 5 total | 345 | 58% |
The OAIC notes that a health service provider generally includes any private sector entity that provides a health service, regardless of turnover. It adds that the finance sector covers banks, wealth managers, financial advisers, super funds and credit providers, also regardless of turnover.
Takeaway: 42% of notifications came from outside the top 5, so no sector gets a pass.
What the table does not tell you
The list counts reports, not risk. A sector can sit high because it holds sensitive records, because many of its members must report, or because it reports well. The OAIC does not rank sectors by how secure they are, and we are not either.
It also covers only notified breaches. Small businesses under $3 million turnover are generally outside the scheme unless an exception applies, so many small incidents never reach this table. Read our breach rules guide for who is covered.
What retail and accounting sites have in common
Both collect names, emails and phone numbers. Both often run a contact form, a booking tool or a customer login. Those are the places to look first.
A short list of checks for your own site:
- Open every form and write down which fields it collects.
- Find out where each form sends its entries and who can read them.
- Remove old plugins and logins you no longer use.
- Make sure your privacy policy matches what the forms really collect. See our privacy policy guide.
Frequently Asked Questions
Which sectors reported the most data breaches from July to December 2024?
Health service providers reported 121 (20% of all notifications), the Australian Government 100 (17%), finance including superannuation 54 (9%), legal, accounting and management services 36 (6%), and retail 34 (6%).
Does a place in the top 5 mean those sectors are less secure?
Not on this data. The OAIC counts notifications from covered entities. A sector can top the list because it holds sensitive data, because more of its members are covered by the scheme, or because it reports more often.
Is a small shop covered by the notification scheme?
Generally not if turnover is $3 million or less, unless an exception applies, such as providing a health service or trading in personal information. Ask your lawyer if you are unsure.
What share of all notifications did the top 5 account for?
345 notifications, or 58% of all 595 received from July to December 2024.
Need a second pair of eyes?
If you want someone to map the forms and logins on your site, see web design in Rockingham or SEO in Rockingham, then get in touch.
Sources
OAIC, Notifiable Data Breaches Report: July to December 2024
. Table 5, top 5 sectors by notifications, and Table 1. Read 3 November 2026.OAIC, Part 4: Notifiable Data Breach (NDB) Scheme
. Source of the small business operator exceptions. Read 3 November 2026.
Last reviewed: 3 November 2026.
Vikas Thakur
Founder of RockingWeb. 16 years of experience from working at TPG, iiNet and Monadelphous, now building websites, software and digital marketing for local businesses in Rockingham and Perth.