Data Breach Rules for Small Business: The 30-Day Clock
Under the Notifiable Data Breaches scheme, a covered business has 30 calendar days to assess a suspected breach. The OAIC logged 595 notifications from July to December 2024. Here is who the scheme covers and what to do first.
 Vikas Thakur Founder, RockingWeb 5 min read
Key takeaways
- A covered business has 30 calendar days to assess a suspected eligible data breach, and the OAIC expects it to finish sooner
- The OAIC received 595 notifications from July to December 2024, up from 518 in January to June 2024
- A breach is notifiable when it is likely to result in serious harm, judged objectively
- Quick remediation can mean no notification is needed, if serious harm is no longer likely
- Small business operators with turnover of $3 million or less are generally outside the scheme, with named exceptions
As at 3 November 2026, the OAIC says a covered entity must take all reasonable steps to finish its breach assessment within 30 calendar days of becoming aware of grounds to suspect an eligible data breach.
Your contact form, booking tool and email inbox all hold customer details. If someone gets into any of them, the clock can start. This guide explains what the scheme asks, who it covers, and what to do in the first hour.
Who the scheme covers
The OAIC describes a small business operator as a business that has not had annual turnover above $3 million in any financial year since 2001. It says these operators generally have no obligations under the Australian Privacy Principles unless an exception applies. The same guidance lists the exceptions, including holding health information and providing a health service, trading in personal information, and opting in under section 6EA of the Privacy Act.
If you are unsure whether you are covered, read our small business privacy policy guide first, then ask your lawyer.
What the OAIC says is notifiable
A data breach is eligible when it is likely to result in serious harm to one or more of the people the information relates to. The OAIC says that needs an objective assessment from the viewpoint of a reasonable person in your position. It also says not every breach is eligible, and if you act fast and serious harm stops being likely, you do not have to notify.
The 30-day assessment window
The OAIC says to treat 30 days as a ceiling. Risk to people often grows with time, so finish sooner where you can. If you cannot finish within 30 days, write down why, show you took all reasonable steps, and show the assessment was reasonable and expeditious.
Takeaway: start writing things down on day one. A dated note beats a memory.
How many breaches the OAIC sees
The OAIC logged 518 notifications from January to June 2024 and 595 from July to December 2024, a total of 1,113 for the year.
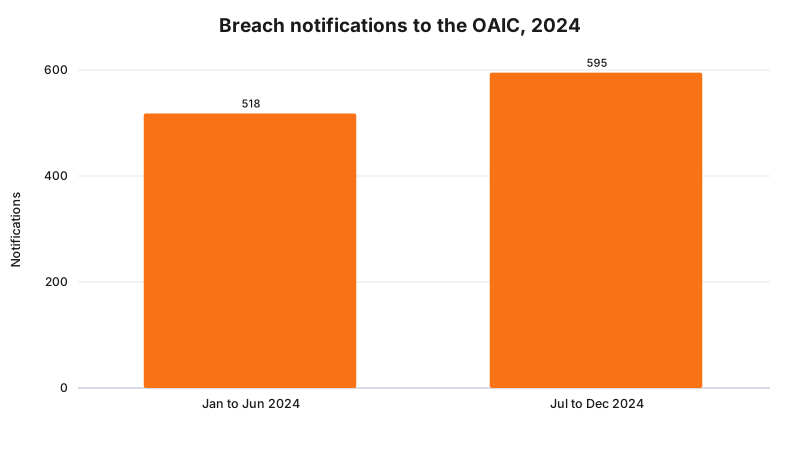
These are notifications from covered entities across all industries, so treat them as a guide to how common breaches are, not a count for small business alone.
Your first-hour checklist
- Note the time you found out and who found it.
- Cut the access: change passwords, remove the user, switch off the form or plugin involved.
- List what data sat in that system, and whose.
- Save logs, emails and screenshots before anyone cleans up.
- Ring your web developer and your hosting provider, and ask what logs they hold.
- Decide who leads the assessment, and set a calendar reminder for day 30.
This is general information, not legal advice. Whether the scheme applies to your business is a question for your lawyer.
Frequently Asked Questions
How long do I have to assess a suspected data breach?
The OAIC says a covered entity must take all reasonable steps to complete the assessment within 30 calendar days after becoming aware of the grounds that caused it to suspect an eligible data breach. It expects entities to treat 30 days as a maximum and finish sooner.
What makes a data breach notifiable?
The OAIC says a breach is eligible if it is likely to result in serious harm to any of the individuals the information relates to. Whether harm is likely is an objective assessment from the viewpoint of a reasonable person in the entity’s position.
Does the scheme cover every small business?
No. The OAIC says generally small business operators, with turnover of $3 million or less, have no obligations under the APPs unless an exception applies. Exceptions include holding health information and providing a health service, trading in personal information, and opting in.
What if remediation stops the harm?
The OAIC says that if an entity acts quickly and, as a result, the breach is not likely to result in serious harm, there is no requirement to notify individuals or the Commissioner.
Want your site checked before something goes wrong?
We can walk through which forms, plugins and accounts hold customer data on your site. Start at web design in Rockingham, or see SEO in Rockingham, then talk to us.
Sources
OAIC, Part 4: Notifiable Data Breach (NDB) Scheme
. Source of the eligibility test, the 30-day rule and the small business operator exceptions. Read 3 November 2026.OAIC, Notifiable Data Breaches Report: July to December 2024
. Source of the 518, 595 and 1,113 notification counts. Read 3 November 2026.
Last reviewed: 3 November 2026.
Vikas Thakur
Founder of RockingWeb. 16 years of experience from working at TPG, iiNet and Monadelphous, now building websites, software and digital marketing for local businesses in Rockingham and Perth.